Tuesday, April 3, 2012

Internet-zugang.at Austrias leading source for ISP cost rating

As i came across i wanted to introduce a friend, Internet-zugang.at.

Internet-Zugang has shown up as an good site for getting news about ISP in Austria so long and also to have an sort of gimmick planned in the near future :)
It's really worth to check it out! Internet Zugang got the actual prizing of Internet Providers in Austria, this is mostly as much worth today as knowing your mobile phone bill!

http://www.internet-zugang.at

Hpefully you will enjoy your stay there and be sure to come back again! Its a sure growing project! Internet-zugang.at

Tuesday, March 27, 2012

Advanced SSH tricks Linux

Today i will show you some SSH tricks that could be usefull! Well ssh is more powerfull than you thoght maybe - so check out the following little helpers to get your ssh life easier!


  • Have you ever tried to mount an filesystem securely over the world wide internetwork :)
    install the small tool SSHFS (apt-get install sshfs)
    You can now mount any remote filesystems DIR you have access to:
    $ sshfs user@remote2:/home/user/documents /mnt
  • Send an Command directly via SSH without login in and have to log out again after execution: this command will simply power off an remote machine!
    $ ssh user@remotehost sudo poweroff
  • If you have any long command you like to execute on an remote system you can also save it to any file as simple text and then run it remotly using:
    $ ssh user@remotehost "`cat filename.txt`"
  • The ssh-copy-id command is not as well-known as it should be, which is a shame because it is a great time-saver. This nifty command copies your public key to a remote host in the correct format, and to the correct directory. It even has a safety check that won't let you copy a private key by mistake. Specify which key you want to copy, like this:
    $ ssh-copy-id -i .ssh/id_rsa.pub user@remote
  • Use ssh-keygen to remove host keys from the ~/.ssh/known_hosts file to save some time. When the remote machine gets new SSH keys you'll get a warning, when you try to log in, that the key has changed. Using this is much faster than manually editing the file and counting down to the correct line to delete:
    $ ssh-keygen -R remote-hostname
  • When you're at the mercy of hotel and coffee shop Internet, a nice secure SSH tunnel makes your online adventures safer. To make this work you need a server that you control to act as a central node for escaping from hotspot follies. I have a server set up at home to accept remote SSH logins, and then use an SSH tunnel to route traffic through it. This is useful for a lot of different tasks. For example I can use my normal email client to send email, instead of hassling with Web mail or changing SMTP server configuration, and all traffic between my laptop and home server is encrypted. First create the tunnel to your personal server:
    $ ssh -f carla@homeserver.com -L 9999:homeserver.com:25 -N

    "this command will open locally port 9999 to static connect to
    port 25 on your remote machine, though that port needs to be
    opened up there, you can now use your mail client or for
    sending mails (port 25 smtp) via your home pc without trouble
    of getting spyed just set your SMTP port in your client to port 9999!
  • Bypass untrusted networks the easy way, lets say you want to browse the web and you have restrictions in your actual network just forward your traffic over ssh:
    $ ssh -D 9999 -C user@homeserver.com

    "now set ip/hostname and port in your Internet Browser eg.
    Firefox and keep on browsing the web securely :)"

Tuesday, March 20, 2012

Be aware of Java ware

"A hard-to-detect piece of malware that doesn't create any files on the affected systems was dropped onto the computers of visitors to popular news sites in Russia in a drive-by download attack, according to Kaspersky Lab. 'What's interesting about this particular attack is the type of malware that was installed in cases of successful exploitation:


It's ideal to stop the infection in its early stages, because once this type of "fileless" malware gets loaded into memory and attaches itself to a trusted process, it's much harder to detect by antivirus programs.'"

Thursday, March 15, 2012

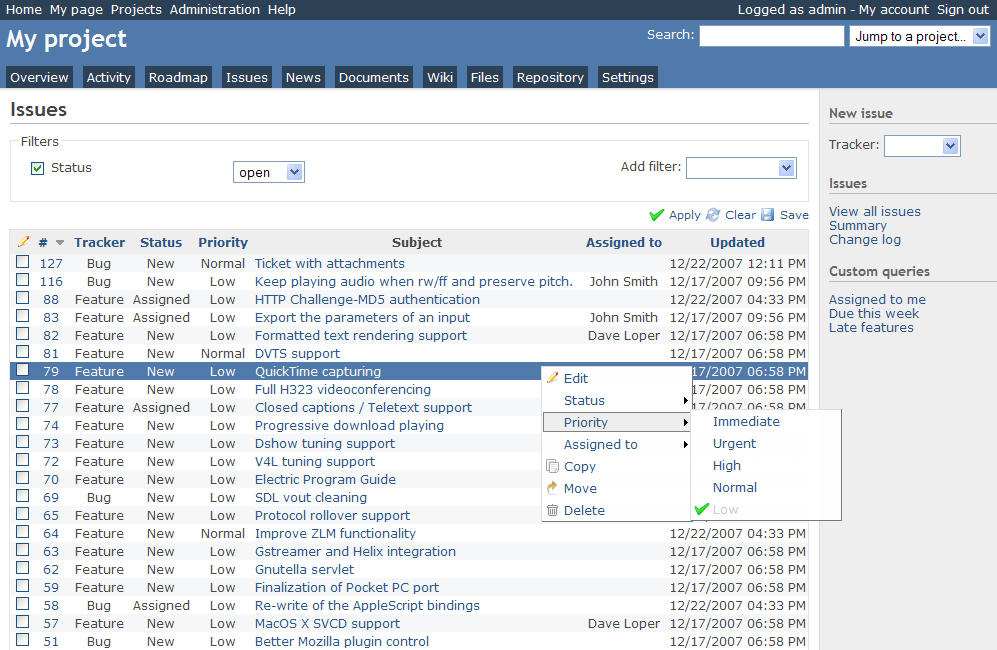
Redmine - apache - ruby - Install in debian >= 5.0

Redmine

Redmine is a flexible project management web application. Written using the Ruby on Rails framework, it is cross-platform and cross-database.

Redmine is open source and released under the terms of the GNU General Public License v2 (GPL).

Some of the main features of Redmine are:

  • Multiple projects support
  • Flexible role based access control
  • Flexible issue tracking system
  • Gantt chart and calendar
  • News, documents & files management
  • Feeds & email notifications
  • Per project wiki
  • Per project forums
  • Time tracking
  • Custom fields for issues, time-entries, projects and users
  • SCM integration (SVN, CVS, Git, Mercurial, Bazaar and Darcs)
  • Issue creation via email
  • Multiple LDAP authentication support
  • User self-registration support
  • Multilanguage support
  • Multiple databases support


First of all make sure you are running an yet stable and configured Apache server.

It will either need mod_cgi or mod_fastcgi to get redmine up and running properly. I prefered mod_f(ast)cgi. Lets check if you already installed these mods:

ls /etc/apache2/mods-available | grep cgi
your result will be something like
cgid.conf, cgid.load, cgi.load, fcgid.conf, fcgid.load

if nothing appears in your output the enter the following commands to install FastCGI:
apt-get install apache2-mpm-worker apache2-suexec php5-cgi libapache2-mod-fcgid
a2enmod fcgid
a2enmod suexec
This will download install and enable the required mods for your apache installation.
To test if they are enabled enter:
ls /etc/apache2/mods-enabled | grep cgi
Yout output should look the same as above when we used mods-available, if so we are ready to go.

Lets go ahead: for this tut i will use Redmine 1.3 yet stable version. So lets go check it out!
(you will need subversion to do this, available in every debian repository)
apt-get install subversion
lets change to our redmine destination directory and fetch it where apache should serve the needed files for the clients:
cd /var/www/yourwebpage/subdomain/httpdocs
(you can choose any other folder you like to share as a webpage, /var/www is just common)
svn co http://redmine.rubyforge.org/svn/branches/1.3-stable redmine-1.3
svn co svn://rubyforge.org/var/svn/redmine/branches/1.3-stable redmine-1.3
Change to the Donwloaded dir and lets have look at the INSTALL File where we can see our dependencies and software that will be needed.
mv 1.3-stable redmine
cd redmine
(nano doc/INSTALL)
well i will Post the Install file here so you dont need to have it opened in your terminal if you use the 1.3 mentioned version of redmine here!

==================================================================
== Redmine installation

Redmine - project management software
Copyright (C) 2006-2010 Jean-Philippe Lang
http://www.redmine.org/


== Requirements

* Ruby 1.8.6 or 1.8.7

* RubyGems 1.3.1

* Ruby on Rails 2.3.5 (official downloadable Redmine releases are packaged with
the appropriate Rails version)

* Rack 1.0.1 gem

* Rake 0.8.3 gem

* I18n 0.4.2 gem

* A database: (only one of these 3 is needed here... i hope you know how to set up MySQL DB!)
* MySQL (tested with MySQL 5)
* PostgreSQL (tested with PostgreSQL 8.1)
* SQLite (tested with SQLite 3)
==================================================================
So lets go get these Programs and appropriate versions running!
apt-get install libapache-ruby1.8 ruby1.8 libgems-ruby1.8 rubygems1.8 libgemplugin-ruby1.8 rails librack-ruby1.8 rake passenger-common libapache2-mod-passenger
Now we have to get our gems for ruby to get things working:
gem sources -a http://production.s3.rubygems.org/
gem sources -u
gem install activerecord -v=2.3.14
gem install actionpack -v=2.3.14
gem install actionmailer -v=2.3.14
gem install activeresource -v=2.3.14
gem install activesupport -v=2.3.14
gem install rails -v=2.3.14
gem install passenger -v=3.0.11
gem install rake -v=0.9.2.2
gem install rack -v=1.1.2
gem install i18n -v=0.4.2
Well done ruby up and runnnig with our needed gems (the first command is for changing the source, you will probybly get an error if you dont do so as debian got a false source provided in standard configuration)

Now follow this guide on the Redmine Production website and you should be good to go to get it running straigt away!
http://www.redmine.org/projects/redmine/wiki/RedmineInstall
or follow me here:


After following this guide you should be able to log into redmin
/etc/init.d/apache2 restart
Apache should be restarted and your redmin should be reachable where you placed it on your webserver! Login with user: admin password: admin

Any questions left? feel free to comment here and give me advice or ask for help!

Wednesday, January 4, 2012

What have I downloaded?

Do you ever wanted to know if you could get harmed by any law for downloading illegally pirated movies apps or music?

In Fact it could be possible that you could get be pleased to charge for someone else!
Most ISP's out there use random IP Adresses (DHCP) out of an IP Pool for they residential customers. So if someone downloaded an pirated movie before you get to this IP Adress you could get harmed through this!
Well i know thats weird but you should have a look at this website:


YOUHAVEDOWNLOADED . COM shows what was downloaded with your IP (only torrent data is collected) but torrent data is the most popular way to pirate stuff!

So be aware and just think of this tiny fact...

In future i will post about correct anonymisation to get rid of such problems and not getting into harm for someone else who does illegal activity ;)

Have a nice Day folks!

Sunday, July 3, 2011

Apply credit card, loans, bad credit, is it safe?


Apply credit card is risky in these days, low interest credit cards shouldnt be given, hackers were always aware of the benefits of the global credit cards suppliers as also the attractive cash back credit cards got into points to be a easy to use cash out service.

Credit card hacking, stealing, selling and frauding is around since ages, as i know its been around since credit cards offers are around. Loans are aspecially developed systems to enslave humans and why shouldnt human missuse this. Someone thought someone got used to it.

As the web presence creditcards.com presents the statistics for the last months most used payments and usements for credit cards.
Credit Card Rate Report

Updated: 06-30-2011
National Average 14.75%
Low Interest 10.73%
Balance Transfer 12.78%
Business 13.07%
Student 13.77%
Cash Back 13.90%
Reward 14.28%
Airline 14.31%
Instant Approval 15.99%
Bad Credit 24.96%

On bottom you can see BAD CREDIT is the main usement of credit cards. These are loans that are payed by fees and are so called throw away credit cards for single use or till the fee amount is reached. These prepayed credit cards opened a new door for cyber crime as they can be used and thrown away as also take place anonymously when only used prepayed. Like Prepayed cell phone cards where used to not get tracked along.
Last day the credit card supplier mastercard.com again got ddosed by the collective anonymouse cause they shut down again the donation account of the wistleblowing platform wikileaks powered by julian assange. In fact the Attack really doesnt damage this huge company - only a few hours customers werent able to get on their page caused by the massive ddos that was running. So long the attacks stopped all the way and the site is accessable again.

Wednesday, June 22, 2011

On line data storage solution dropbox code fails, logins messed!

The on line data storage data backup service DROPBOX got in serious security trouble this week.
on line data storage backup service
Dropbox op posted on their blog that a massive security hole because of trouble with dropbox codes occured - every user of the storage service was able to log in with any password in any account - the security of the storage service totally failed and let every user in and take a look at any data provided on the internet backup service.

For over 4 hours the error was present and the backup service provider claims that around 1% of users logged in in this time to their drop box account. So maybe there happened no violation or abuses.
everythings alright
In fact be care when uploading data any where to the net or any online storage provider! As long they are not encrypted your data can seriusly be harmed or abused!

Thursday, June 9, 2011

Internet phone services skype , sources sold to russia!

The internet phone service skype, which is an voip service, not an business voip at all but a realiable cheap voip service for personal use.
voip service
 In fact phoning from one skype user to another is for free, as most internet phone services out there, best way of usage is via broadband, so call it broadband phone if you like to.

broadband voip services
 The russian new vedomosti and the press agency bloomberg are today talking about an cooperation between microsofts skype and the russian secret service FSB. If its real what they say, microsoft is willing to handle out parts of the source code to FSB, wouldnt be nice in any way... KGB reloaded!
voip kgb
So this VOIP service got compromitted! RIP, the code will be out all over soon i think.

GVU accident , DDOS started site down , a few hours after Kino.to got busted!

GVU webpresence is accidentially not reachable anymore, the reason is it got DDOSD obviously by fans of Kino.to cause the site got down a few hours after the message made it around the globe that 13 people where looked up in jail, including the operator of kino.to
404

The servers seem up now again but the DDOS remained the whole night until 8am in the morning, some statements are also readable around the net saying "We will be back" obviously posted by members of the platform kino.to.
ddos tux

by the way check out g-stream.in you would probably like the site if you where a kino.to fan.

Wednesday, June 8, 2011

Kino.to raid and busted, 13 People arrested!

Kino.to is dead for now! Accident happend lawyer needed!

Kino.to has today been defaced and the page has been replaced by the german criminal police!
More than 250 Police officers 20 Special forces for internet security and information raided the whole company.
Further many streamhosting pages got taken down as well, they didnt get raided by the police train accident, but many providers closed their web presence.

Police demands their work with:
To raise suspicion development of an criminal organisation to commercial handling of illegal or copyrighted material and in effect getting funds from this system. simply: copyright violation

in long study case, police found that kino.to hosts many streaming hosts by itself to keep the site running so they are directly  responsible for most of the content they hosted!


Layer 8 train accident attorney , technic works human failed!

As for now i bring this back up cause i want to show again human brains are tend to fail machines ever work their process, train accident humans can be train d to override accidents but as here in attorny this failed.
 Poor fail again when humans fail at computing or at operating machines, terribly this happens in the worst case when  humans do big things, flying a jet plane, driving a train, moving a crane - for this case every of this big big machine has its own technical system to help the user out when his brain cant get it anymore. Train accident could probably be stopped by a pedal the driver always has to push to keep the train running or as its on air jet plane the pilot needs to be in contact with an tower or officer to make sure he is a awake and alife.
Accident claim could be a big fail and also in future it could harm innocent people, so in this case get a lawyer probably an accident lawyer to fit and fight your rights.

26 people were killed and approximately 130 more were injured when a Metrolink commuter train crashed head-on into a freight train outside of Los Angeles on September 12, 2008. The crash may have been preventable, as preliminary investigations are revealing that the Metrolink conductor failed to stop at a red signal. Even more devastating is the fact that the conductor’s failure to stop could have been due to him being distractied while text messaging.

Damn  this got me to think, cheers folks and check your insurances ;)

Tuesday, June 7, 2011

Graphic cards gpu technology breaks passwords faster than every cpu!

I got around the progtram IGHASHGPU  and rapidly found that graphic cards gpus shouldnt be underrated these days! 
ighashgpu

An AMD Radeon 5770 can crack an standard password with 5 characters in under one second, a normal cpu with about 3GHz would need to spend about 24 seconds on thsi operation.
Another password with about 6 characters uses an normal CPU about 1 and a half hour, while the GPU of the Radeon 5770 manages to crack this word in ~4 seconds.
With an passwort with 7 chars where one is an space, an normal CPU would need about 75 days for this operation, our GPU fucks the password up in about ~7 hours! 
multiple gpu


So in future if we think of an SLI moded Graphiccard with more power than this mid-range card we used here, passwords could be breaked really fast in no time, what took as about 50 years for now can be done i about 5 weeks or less depending on the GPU powers...


so long here is an crack report of multiple GPUS with IGHASHGPU:
for example, result for HD5770+HD4770+8600GT looks like:

****************************************************************
***      MD4/MD5/SHA1 GPU Password Recovery v0.70.48.4       ***
***    For ATI RV 7X0 cards and nVidia 'CUDA' ones (G80+)    ***
***      (c) 2009-2010 Ivan Golubev, http://golubev.com      ***
***             see "readme.htm" for more details            ***
****************************************************************
*** Any commercial use of this program is strictly forbidden ***
****************************************************************

Found 2 CAL device(s)
Found 1 CUDA device(s)
Starting brute-force attack, Charset Len = 36, Min passlen = 4, 
Max passlen = 7
Charset (unicode -> 0) [abcdefghijklmnopqrstuvwxyz0123456789]
Charset in HEX: 61 62 63 64 65 66 67 68 69 6a 6b 6c 6d 6e 6f 
70 71 72 73 74 75 76 77 78 79 7a 30 31 32 33 34 35 36 37 38 39
Starting from [aaaa]
Hash type: MD5, Hash: cbe1d6d5800ec1e03a5f2a64882a0d41
We're running at ATI and NVIDIA GPUs simultaneously.
Device #0: [RV830] 850.00 Mhz 800 SP
Device #1: [RV7x0] 750.00 Mhz 640 SP
Device #2: [GeForce 8600 GT] 1188.00 Mhz 32 SP
Hardware monitoring disabled.
CURPWD: 66owsnc DONE: 51.02% 
ETA: 13s CURSPD: 2756.0M=1646.0M+1017.4M+92.6M
Found password: [roger15], HEX: 72 6f 67 65 72 31 35
Processed 42 228 252 672 passwords in 16s.
Thus, 2 731 452 307 password(s) per second in average. 
Gert some GPUS get yourself an lawyer, an insurance, some passwords and crack the hell out of em! CHEERS
Tramadol
 As my picture above describes, i will get me a bunch of tramadol or zolpidem and chill out till my 12 char pw got cracked =P cheers folks!

Monday, June 6, 2011

Cisco announces filesharing technology will hit upwards till 2015!

Cisco announces filesahring and its traffic will double up till 2015.

Cisco announces a new study in technology around the internet every few years and thsi year the news tell us that file sahring will go straight upwards and double up till 2015.
Sharing grows in an big dimension, long story short this is what Ciscos Visual Networking Index told us.


Constructive Economy tries to set file sharing to an state of an bad view, it tries to promote it as something simple cruel bad, but they fail in any way :) sharing isnt that bad and its the main part of the internet.

In 2015 there should flow about 13.797 Petabyte around the globe for filesharing
and in 2010 it was around 5.000 Petabyte - this upgoing traffic is massive.

Friday, June 3, 2011

Sony got hacked again and again and again...

Yesterday a new sony hack came up, the company got hacked again and around 20.000 free music coupons and user data has been released on the web. Another massive leak and it seems that sony really doesnt care about security nor their users and payers...

_____|\                    
              _.--| LOL |:                    
             <____|.----||                    
                    .---''---,                
   The               ;..__..'    _...         
    Lulz           ,'/  ;|/..--''    \        
     Boat        ,'_/.-/':            :       
            _..-'''/  /  |  \    \   _|/|     
           \      /-./_ \;   \    \,;'   \    
           ,\    / \:  `:\    \   //    `:`.  
         ,'  \  /-._;   | :    : ::    ,.   . 
       ,'     ::   /`-._| |    | || ' :  `.`.)
    _,'       |;._:: |  | |    | `|   :    `' 
  ,'   `.     /   |`-:_ ; |    |  |  : \      
  `--.   )   /|-._:    :          |   \ \     
     /  /   :_|   ;`-._;   __..--';    : :    
    /  (    ;|;-./_  _/.-:'o |   /     ' |    
   /  , \._/_/_./--''/_|:|___|_,'        |    
  :  /   `'-'--'----'---------'          |    
  | :     O ._O   O_. O ._O   O_.      ; ;    
  : `.      //    //    //    //     ,' /     
~~~`.______//____//____//____//_______,'~     
          //    //~   //    //                
   ~~   _//   _//   _// ~ _//     ~           
 ~     / /   / /   / /   / /  ~      ~~       
      ~~~   ~~~   ~~~   ~~~ 
 
The LULZSEC crew has broken into
„Sony Pictures International“ 
„Sony Music Netherland“ 
„Sony Music Belgium“ 
 
 
Actual news about the leak can be found here: 
http://twitter.com/#!/lulzsec
 
LULZSEC announced that the are waiting for some donations 
via bit coins yesterday evenening.
Today at 10:00 am they posted: "We will take a break and 
then the hacks will continue, thnaks for donation"
Really another bad sad day for the sony entertainment 
system and their workers
especially the security advisors ;) 

Mac Defender kills Apples Security!

The well known scareware mac defender that has been around the last few days, was to be killed by Mac OSX Security Update 2011-003 but the scareware developer team killed the security suite within 8 hours! Apples Security suite isn't able to track MAC Defender anymore and the app looks legit again.
A new race has began between Mac OSX Developers and the on the come scareware team. Windows users now can look at apple mac osx with an smile ;) the malware future has begun and there are more to come!

Wednesday, June 1, 2011

Next level Cyberwar is coming up!

Cold war is approaching again,
this time the war starts on another level, on the world wide web overall the planet. Nations begin to recruit and train personal especially for cyber war bzw counter cyber war. I think many big Companys are involved cause the most well trained computer experts on our planet rule the security in such companies. Training new people is definatly impossible if you want em to learn security technics @ computing without relaying knowledge.
So this is the point where the recruiting jumps in.
2 Countries are rapidly starting to recruit computer experts in security especially for cyber fights and domination on the internet.

Today we have KOREA vs BRITAIN


KOREA

BRITAIN

 Im still wondering what this will be in the end but im sure - cyber is on the come - and we are in the middle of it ;) maybe an MITN should be globally done.

WE are watching you the globe is fully wired, the forces are able to get everywhere, no mountain, no hill, no sea, no river can stop us - the globe is wired.

Go Britain !
Im acting patriotic here, tell me what you think.

Cheers folks

Tuesday, May 31, 2011

Fujitsu Siemens's Erase Disk launched!

The Company Fujitsu Siemens Augsburg has invented an new Addon to all their mobile computer series. An tool called "erase disk" is implemented in bios and uefi.


With this tool its possible to erase your whole disk with 5 different algorythms that will wipe anyhting out of them.
First i thought, umm nothing special, but to do a normal disk erasment you need a proper running OS or an boot disk with the lagorithms on it to delete a disk.
With Fujitsus new tool "erase disk" its possible to erase any disk though in that case if no OS or no proper installed OS is running on the Notebook/Computer
The 4 used algorythms are:
  • Zero Pattern (1 pass) 
  • German BSI/VSITR (7 passes)
  • DoD 5220.22-M ECE (7 passes) 
  • Guttmann (35 passes)
This will depending on disk space take 1 to 10 minutes per Gigabyte for erasment.

With this tool its possible to wipe IDE, SATA including Raid systems but no solid state drives.

Fujitsu has invented an real economy product here, i can remember when a disk of mine was broken i always borke it a lot more to get it wasted unrecoverable and the moved to trash that nobody can find it =P

Cheers folks!

Monday, May 30, 2011

Super Injunction, twitter failed

Twitter just gave away the whole user information of an member that posted news in the UK that shouldnt have shown up.
The UK uses a system or let me call it an "take-down" law that gives the government the right to take down any News they dont want to appear or be spoken out. If the Super Junction is called no one is allowed to talk or write about the happening in free places or newspapers nor on the Internet eg. Twitter.

So now on Twitter always committed and said no our users are safe, today is a bad day for twitter.

Long story short - if you post on twitter you could be charged for any post you ve done, twitter wont keep your account information safe...

Thursday, May 26, 2011

Apple Iphone 4 hardware hacked!

Finally the Iphone 4 hardware got hacked and is now open for everyone.
Apple used an 256-Bit key to encrypt any data stored on the phone, GPS-Data, Usernames and passwords, phonebook entries, messages, etc... and all other related user data that is stored on the phone.

This new revealed hack now allows us to do a Backup of an apple iphone 4 and also decrypt this backup to get the data out of this solid box.

As they claim Russian company ElcomSoft has done this hack first and created an easy to use software for everyone. ElcomSoft


An sheet here shows what is possible with the light and the full edition of this software:

ElcomSoft offer this iOS 4 forensic toolkit to security and law enforcement agencies, but anyone can purchase the software to extract the encrypted data on a device.

Wednesday, May 25, 2011

MeeGo 1.2 Release

The new replacement on mobile phones like the Nokia N900, N8 and N9, MEEGO will establish in future instead of Maemo.

Also this newly improved peace of software will be available on most Netbooks / laptops for use.
To take a look at the Design click the next picture:
Simple to handle OS for netbooks


The MeeGo 1.2 Core OS provides a complete set of enabling technologies for mobile computing.

Some highlights of the MeeGo Core stack include:
  • MeeGo Reference Kernels supporting a variety of Intel Atom and ARMv7 platforms.
  • QML Application Framework and extended Qt-Mobility APIs, including additional location, system, connectivity, and sensor/haptic capabilities for rapid, rich, application development.
  • Enhanced Telephony and Connectivity capabilities, including:
    • GSM, GPRS, and HSPA+ network support
    • SIM Application Toolkit
    • Expanded Bluetooth profiles
    • Expanded VPN and wireless authentication methods
    • USB, WiFi, and BT-PAN data tethering capability
    • Enhance multimedia support, including RTSP streaming with progressive download

This release also includes the following: